Flagship project
SIEM Home Lab
A Splunk or Wazuh lab collecting logs from Windows and Linux machines.
- Wireshark
- Kali Linux
- Windows
4.7/5
Student rating
6
Structured modules
4+
Portfolio projects
Yes
Placement support
A SOC analyst watches an organisation's security alerts, separates real attacks from noise and escalates what matters. This course trains that daily workflow on real tools, from log sources to a written incident report.
The soc analyst programme at techcadd Amritsar is built the way the work is actually done: you handle the data, train and break the models, then ship something that runs. Tools such as Splunk, Wazuh, Wireshark are installed on your own machine in week one, not shown on a slide in week ten.
It runs across 2 – 3 months with morning, evening and weekend batches, and every module closes in a reviewable artefact. By the end you hold a certificate, a portfolio, and the ability to talk through your own decisions in an interview for a soc analyst (l1) role.
There is no entrance test and no restrictive prerequisite. What follows is what the programme actually checks for before you enrol.
Job titles vary by company, but the underlying expectations do not. Each destination below maps to work you will have already done during the programme.
Most soc analyst training in this region stops at the tutorial: you follow along, the notebook runs, nothing is retained. This programme is built the other way round — every module hands you an unfinished problem and a deadline, and a mentor reviews what you did with it.
That is slower and harder than watching lectures. It is also the only version that survives an interview, because the questions there are about the decisions you made, not the code you copied.
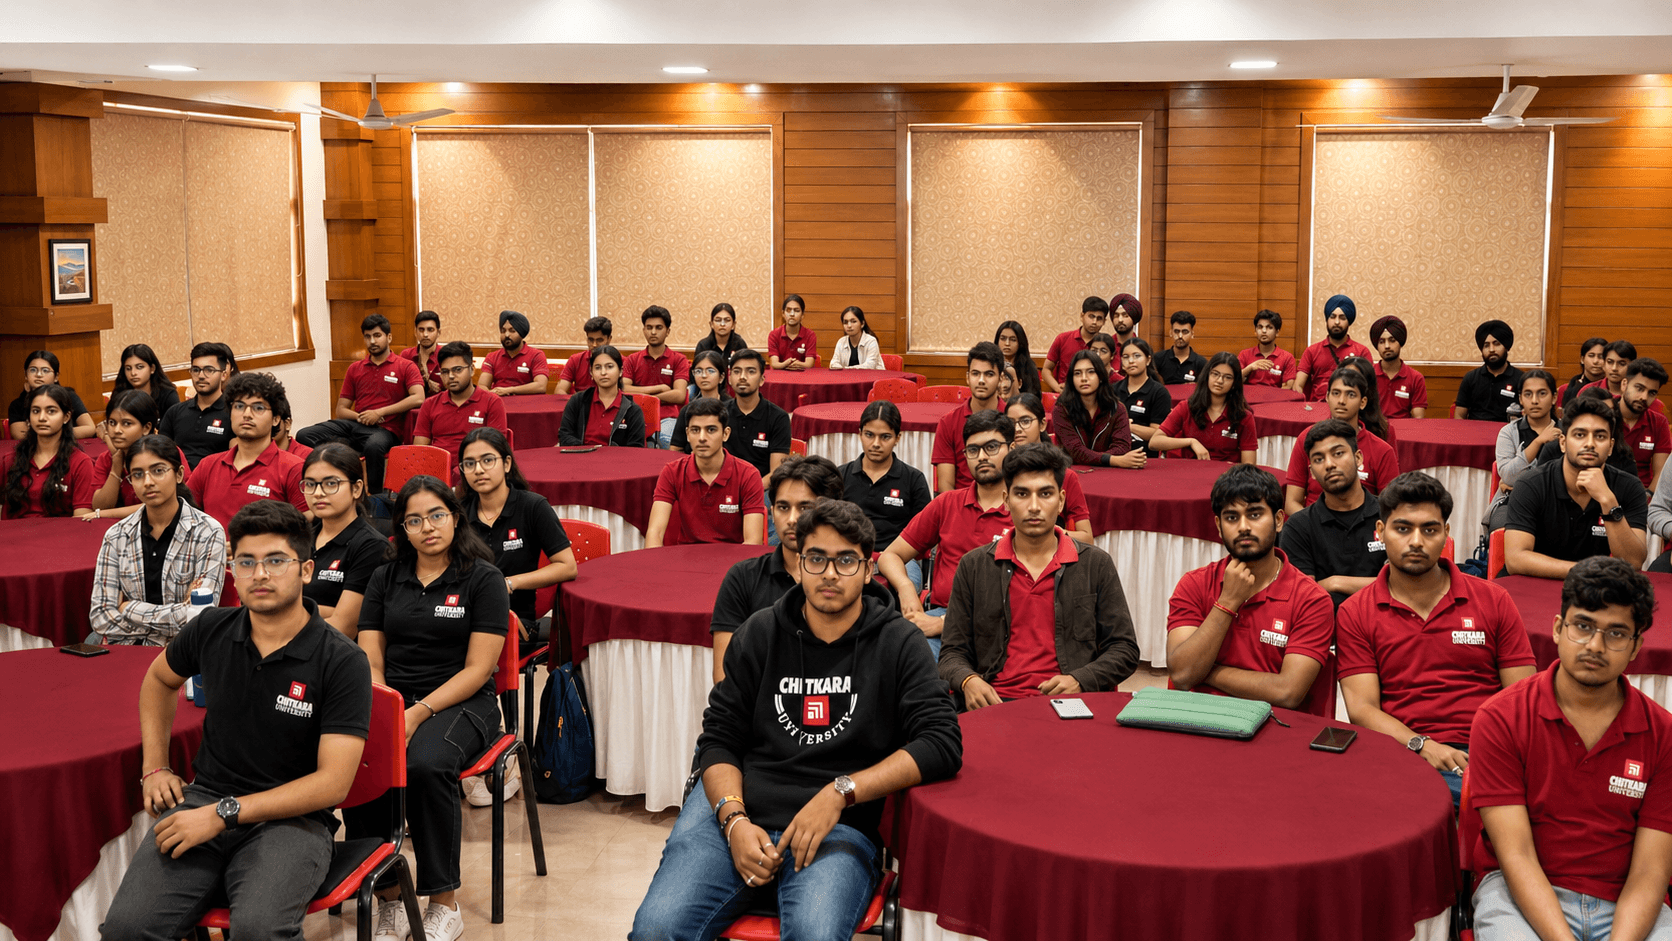
Project review week at the Amritsar campus
Mentors mark up work line by line
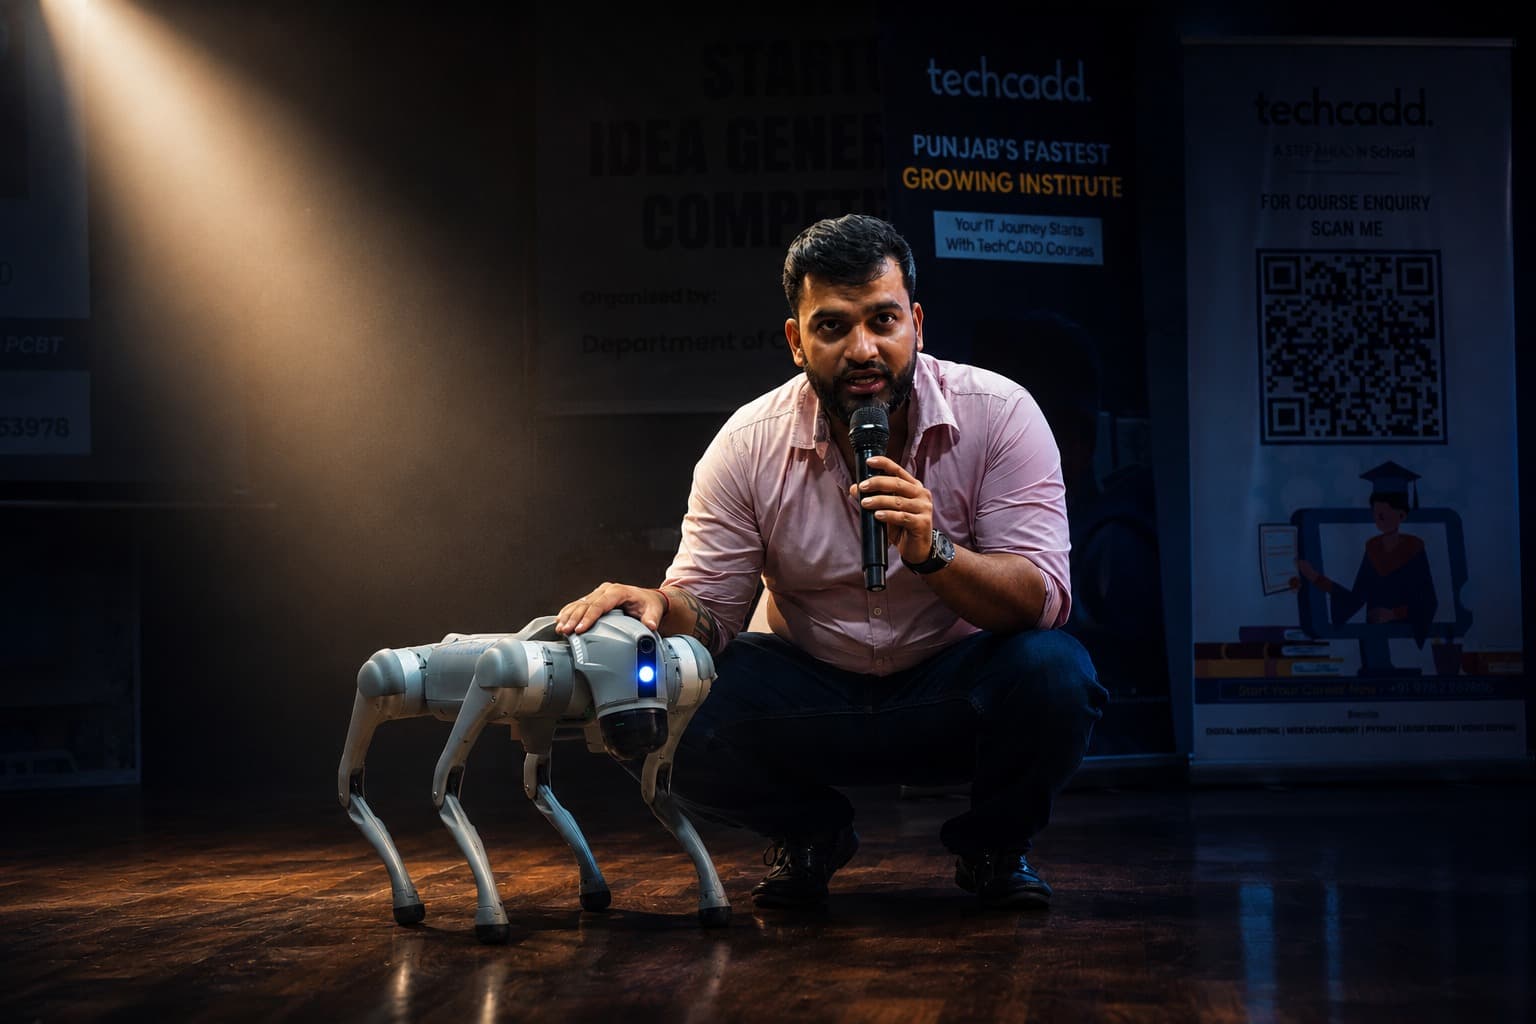
Hiring drive & mock interview day
Practitioners run the panel, not HR
Every tool below is installed, configured and used by you during the course — not demonstrated on a slide. You leave able to set up your own environment from scratch.
8tools covered
Issued on completion against the modules you finished and the projects you submitted — plus an internship letter where the industrial training track applies. Shareable to LinkedIn, and verifiable by an employer who calls the Amritsar desk.
Security & SOC Fundamentals is where the SOC Analyst track gets its footing. You work the concepts in the lab first, then carry them straight into the running project rather than leaving them as isolated exercises.
A reviewed piece of work demonstrating how a soc operates and tiers, shifts and escalation.
A certificate answers what you can do today. This is the honest answer to what soc analyst looks like three to five years out, and why the fundamentals this course spends real time on are what carry you there.
The 2 – 3 months programme is built around the part that is genuinely in your hands — and you leave holding all of it.
A reviewed portfolio, an industry-recognised certificate and a fundamentals-first foundation you can keep building on. Markets move, as they always have; that foundation is exactly what lets you move with them as cyber and cloud work around you keeps shifting.
A Splunk or Wazuh lab collecting logs from Windows and Linux machines.
A suspicious email traced from header to payload with a written verdict.
Alerts from a lab modelled on a real techcadd client environment, triaged and escalated.
A simulated breach investigated end to end and documented for management.
Every project moves through the same loop: understand the brief, build it with guidance, then explain the decisions behind your work. The certificate is the receipt — the portfolio is the point.
Break a real requirement into a plan, the constraints it has to live inside, and the right tool for each part of it.
SIEM Home Lab
Work hands-on with trainer feedback arriving while the decisions are still cheap to change.
Phishing Investigation
Turn the finished work into a portfolio story you can defend line by line in an interview.
Live SOC Brief
Two decades of training in Amritsar, in a format that has not changed since: small batches, real projects, mentors who still work in the field.
Your mentor works in soc analyst for a living. The examples in class come from that work, and so do the shortcuts.
Batch sizes are capped so a raised hand gets answered in the session it was raised in, not weeks later.
Every submission comes back annotated, line by line. The notes are the point — they are what you carry into the interview.
We teach Splunk, Wazuh, Wireshark and refresh the list each intake, because a stale stack is worse than no stack.
Morning, evening and weekend tracks, classroom or live online, with recordings either way for revision.
Resume and portfolio review, mock interviews and hiring-drive access — and it does not stop the day the course ends.
Collected from students who completed the soc analyst programme at the Amritsar campus, across morning, evening and weekend batches. Hover a card to stop the row and read it.
4.7
out of 5
205 verified reviews from Amritsar students
I joined the SOC Analyst batch with almost no background, and what made the difference was that security & soc fundamentals was taught by building rather than by slides. By the third week I was debugging my own code instead of copying someone else's.
The project reviews are the real value. My phishing investigation was picked apart line by line, and those notes are exactly what I ended up talking through in the interview that got me a security monitoring analyst offer.
Weekend batches meant I kept my job through the whole 2 – 3 months. Anything I missed got re-explained without fuss, and lab access outside batch hours was never a problem.
VirtualBox and the rest of the stack were set up on day one, so no week went into environment issues. Batches are small enough that a doubt gets answered the same day instead of piling up.
I had tried learning soc analyst on my own twice and stalled both times. A fixed batch in Amritsar, a mentor who checks your work and a deadline on every module is the only reason I finished.
Placement support was not just a line on the brochure — resume and portfolio review, two mock interviews with people who do the job, and a referral into one of the hiring drives.
The syllabus is current. We worked in Ubuntu Linux rather than the older tooling most soc analyst syllabi around here still teach, and that came up directly in my first interview.
The balance of theory to lab time is about right: enough to understand why something works, then straight into building. I left with 4 projects I can demo, not just a certificate.
If something here is not covered, the Amritsar desk will answer it directly — no call-back queue.
No. The programme opens at beginner level and assumes no background beyond comfort with a computer. Students who already have some exposure move through the early modules faster and spend the saved time on project work.
Book a free demo class and see the lab before you decide.