Flagship project
Full Lab Penetration Test
A scoped test of a lab network delivered as a professional report with severities.
- Wireshark
- Burp Suite
- Metasploit Framework
4.7/5
Student rating
15
Structured modules
3+
Portfolio projects
Yes
Placement support
Cybersecurity is becoming an important career field as businesses, websites, applications, networks, and digital systems increasingly need protection from cyber threats. Techcadd's Ethical Hacking Training in Amritsar is designed for students and beginners who want to understand how cybersecurity works and develop practical skills for identifying and securing vulnerabilities.
The training introduces learners to important ethical hacking concepts, networking fundamentals, system security, web security, vulnerability assessment, penetration testing, and commonly used cybersecurity tools. The focus is on learning security techniques responsibly and applying them only in authorized and controlled environments.
Whether you are a 12th-pass student, graduate, IT learner, fresher, or working professional, ethical hacking training can help you build a foundation for careers in cybersecurity and information security. Practical learning, guided exercises, security tools, and project-based exposure can help students move beyond theoretical knowledge and understand how cybersecurity is applied in real-world situations.
If you are searching for an ethical hacking course in Amritsar with a career-focused learning approach, Techcadd can be a starting point for developing relevant cybersecurity skills and exploring future opportunities in ethical hacking, penetration testing, security operations, and related IT roles.
One of the biggest advantages of learning ethical hacking is that you do not necessarily need to be an experienced cybersecurity professional to start. A well-structured ethical hacking course in Amritsar can begin with networking, operating-system and security fundamentals before progressing toward vulnerability assessment, penetration testing and ethical hacking techniques.
Job titles vary by company, but the underlying expectations do not. Each destination below maps to work you will have already done during the programme.
Most ethical hacking training in this region stops at the tutorial: you follow along, the notebook runs, nothing is retained. This programme is built the other way round — every module hands you an unfinished problem and a deadline, and a mentor reviews what you did with it.
That is slower and harder than watching lectures. It is also the only version that survives an interview, because the questions there are about the decisions you made, not the code you copied.
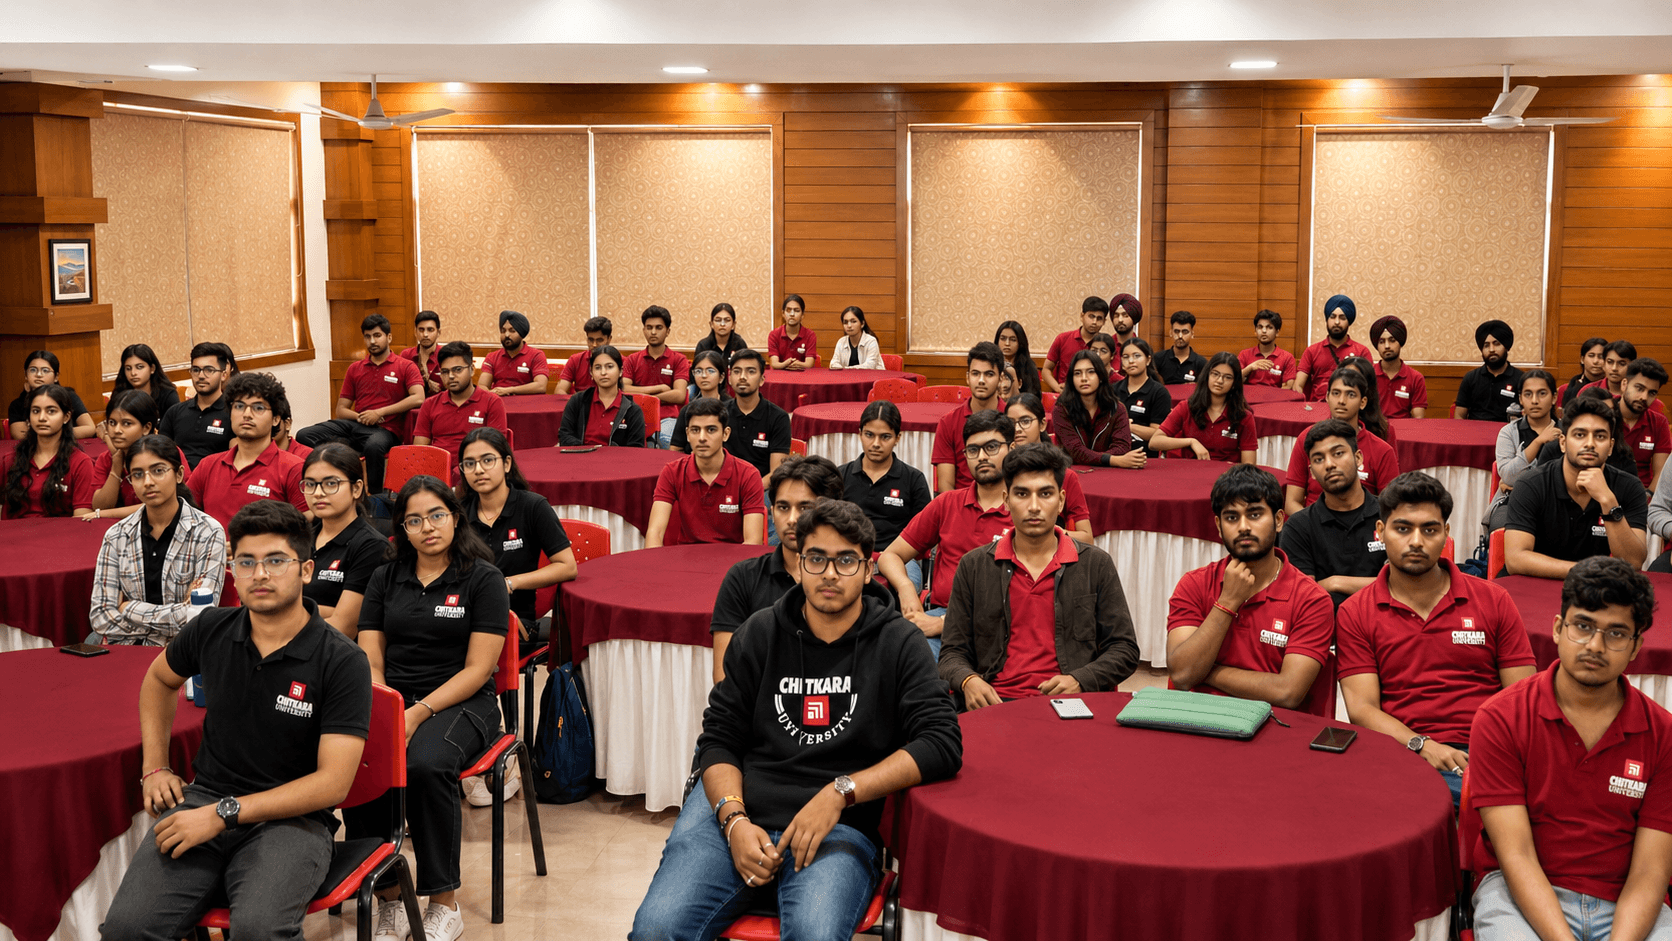
Project review week at the Amritsar campus
Mentors mark up work line by line
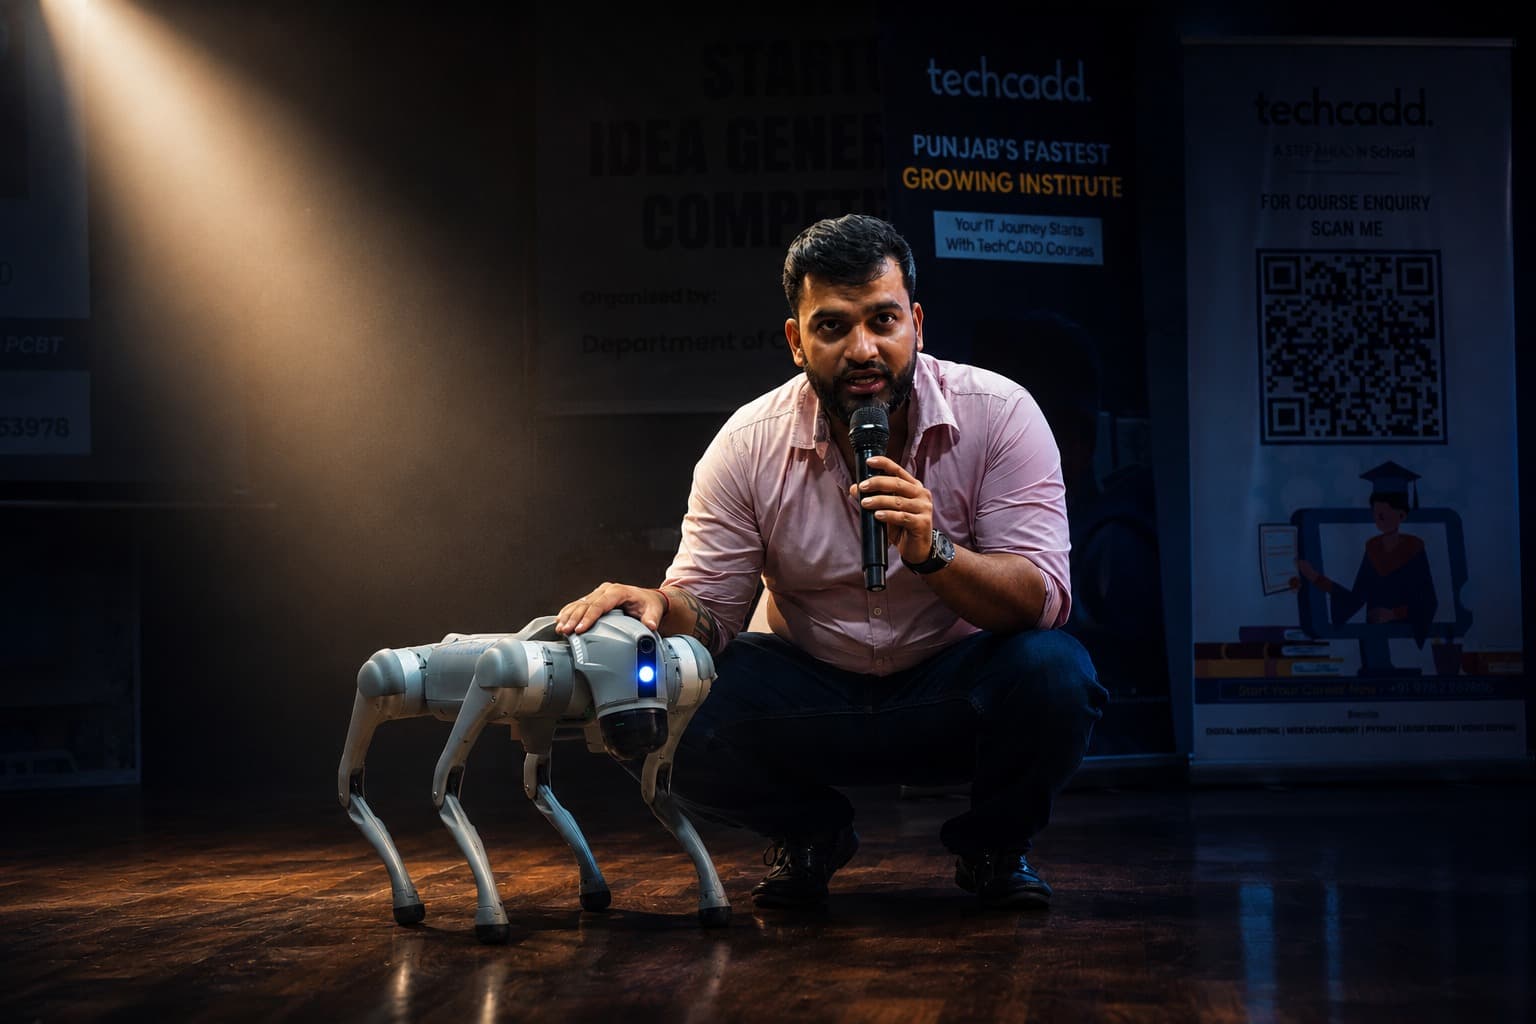
Hiring drive & mock interview day
Practitioners run the panel, not HR
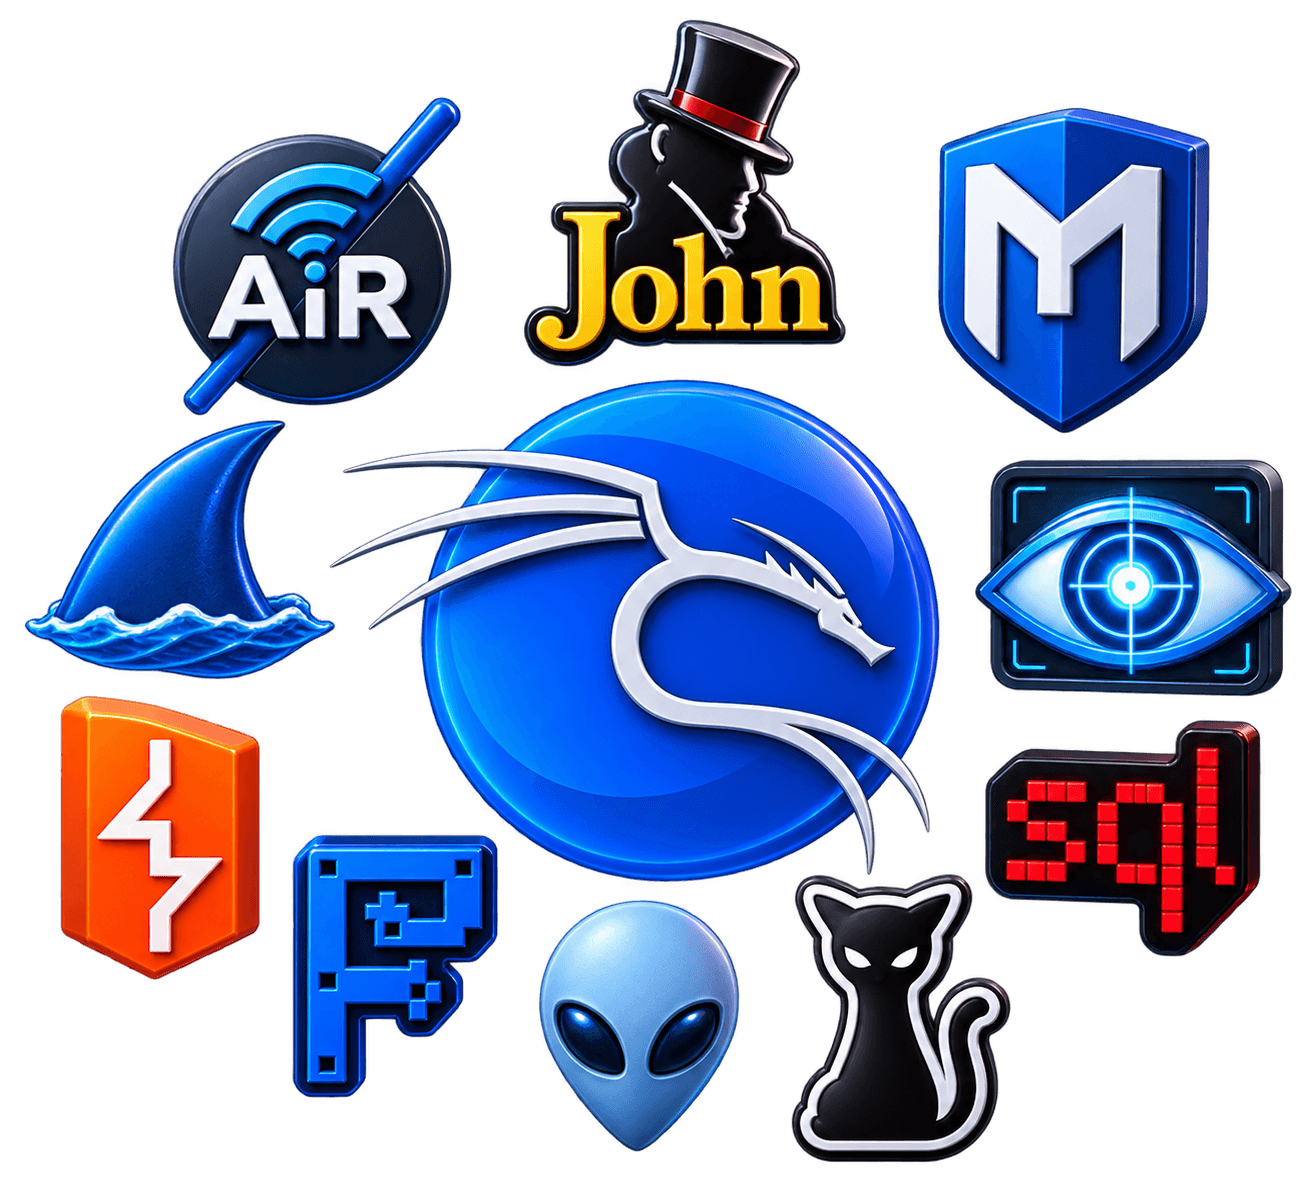
Every tool below is installed, configured and used by you during the course — not demonstrated on a slide. You leave able to set up your own environment from scratch.
8tools covered
Issued on completion against the modules you finished and the projects you submitted — plus an internship letter where the industrial training track applies. Shareable to LinkedIn, and verifiable by an employer who calls the Amritsar desk.
Students begin by understanding the basic concepts behind cybersecurity, including information security, cyber threats, vulnerabilities, risks, authentication, authorization and security controls. This foundation helps learners understand why organizations need to protect systems, applications, networks and data.
The vocabulary and the threat model everything later in the course is judged against.
A certificate answers what you can do today. This is the honest answer to what ethical hacking looks like three to five years out, and why the fundamentals this course spends real time on are what carry you there.
The 4 – 6 months programme is built around the part that is genuinely in your hands — and you leave holding all of it.
A reviewed portfolio, an industry-recognised certificate and a fundamentals-first foundation you can keep building on. Markets move, as they always have; that foundation is exactly what lets you move with them as cyber and cloud work around you keeps shifting.
A scoped test of a lab network delivered as a professional report with severities.
A structured assessment of a vulnerable app with reproducible proof-of-concept steps.
An authorized system assessed and documented — findings, impact, evidence and remediation.
Every project moves through the same loop: understand the brief, build it with guidance, then explain the decisions behind your work. The certificate is the receipt — the portfolio is the point.
Break a real requirement into a plan, the constraints it has to live inside, and the right tool for each part of it.
Full Lab Penetration Test
Work hands-on with trainer feedback arriving while the decisions are still cheap to change.
Web Application Assessment
Turn the finished work into a portfolio story you can defend line by line in an interview.
Vulnerability Assessment Report
Ethical hacking is not simply about learning commands or using security tools. A strong learning program should help students understand how networks, systems and applications work, where vulnerabilities can occur, how security testing is performed responsibly, and how organizations can reduce cyber risks. Techcadd's Ethical Hacking Training is designed around this career-focused approach, helping learners gradually move from foundational concepts toward practical cybersecurity skills.
Beginners often make the mistake of starting directly with advanced hacking tools. Without understanding networking, operating systems and security fundamentals, it becomes difficult to understand what the tools are actually doing. A structured ethical hacking program should therefore start with the basics — computer and networking fundamentals, TCP/IP concepts, network protocols, Linux fundamentals, Windows security concepts, cybersecurity terminology, authentication and access control, vulnerability concepts, web security fundamentals and security testing methodologies. This foundation makes advanced topics easier to understand and gives students knowledge they can continue using throughout their cybersecurity career.
Cybersecurity is a practical field. Reading about a vulnerability is useful, but understanding how security testing works in a controlled laboratory environment can make the concept much clearer. A career-oriented ethical hacking course should give learners opportunities to work with security tools and simulated environments — Kali Linux, Nmap, Wireshark, Burp Suite, Metasploit and vulnerability-scanning utilities, depending on the training curriculum and laboratory setup. The objective is not simply to memorize commands. Students should understand what each tool is used for, what information it provides, how to interpret results and how security professionals use those results to improve security.
One important area of cybersecurity is identifying weaknesses before attackers can exploit them. Vulnerability assessment introduces students to the process of identifying potential security weaknesses in authorized systems. Students can learn concepts such as asset identification, attack surface, vulnerability discovery, security scanning, risk evaluation, vulnerability prioritization, basic remediation concepts and security reporting. This helps learners understand the difference between discovering a vulnerability and responsibly communicating the issue so that it can be addressed.
Students who want to move toward professional cybersecurity roles may eventually explore penetration testing. Penetration testing involves authorized security assessments designed to identify and demonstrate security weaknesses. A structured program can introduce learners to the stages involved in security testing, from information gathering and reconnaissance through vulnerability analysis, controlled exploitation concepts and reporting. The emphasis must remain on authorized environments. Ethical hacking should never mean attempting to access another person's account, website, server or network without explicit permission. Professional cybersecurity requires technical ability combined with legal and ethical responsibility.
Linux and networking knowledge can be extremely valuable for cybersecurity learners. Students working toward ethical hacking careers often need to understand IP addresses, ports, protocols, DNS, HTTP and HTTPS, firewalls, routing, network services, Linux commands, file permissions, processes and system administration basics. These concepts provide the technical foundation needed to understand security tools and security events. Instead of learning isolated commands, students should learn why a command is being used and what its output means.
Modern businesses rely heavily on websites and web applications. As a result, web application security is an important part of cybersecurity education. A structured course can introduce learners to concepts associated with common web security weaknesses, including authentication issues, authorization problems, input validation weaknesses and other application-level vulnerabilities. Students can use controlled lab environments to understand how vulnerabilities occur and how developers and security teams can mitigate them.
Tools are an important part of practical cybersecurity learning, but tools alone do not make someone a cybersecurity professional. Students can benefit from understanding what different categories of tools are designed to accomplish. Nmap can be used for network discovery and security auditing. Wireshark helps learners examine and analyze network traffic. Burp Suite is widely used for testing web applications. Metasploit Framework provides a platform used for security testing and vulnerability research in authorized environments. Kali Linux provides a security-focused operating-system environment containing many tools used for security assessment and testing. Learning these tools within a controlled lab gives students a safer environment to practise without interfering with real systems.
Cybersecurity is rarely about following one fixed set of steps. A security professional may encounter incomplete information, unexpected configurations, unusual network behaviour or vulnerabilities that require investigation. That is why an effective ethical hacking program should encourage students to think analytically. Instead of simply asking "which command should I run?", students should learn to ask "what am I trying to discover, why is this information important, and what should I investigate next?" This problem-solving mindset can become one of the most valuable skills developed during cybersecurity training.
Ethical hacking training does not limit a learner to one specific job title. Depending on their education, practical skills, experience and additional certifications, learners can explore career paths such as Cybersecurity Analyst, Security Analyst, Junior Penetration Tester, Vulnerability Assessment Analyst, SOC Analyst, Information Security Associate, Network Security Associate, Security Testing Assistant and IT Security Support. Actual job requirements vary by employer, so students should continue building practical experience, communication skills and relevant technical knowledge.
For students searching locally for an ethical hacking course in Amritsar, classroom or guided training can provide a structured environment for learning difficult technical concepts. Students can benefit from instructor guidance, practical exercises, troubleshooting support and interaction with other learners. This can be especially helpful for beginners who may otherwise find cybersecurity overwhelming when learning entirely independently.
The purpose of ethical hacking training should be broader than completing a syllabus. Students should leave the program with a clearer understanding of cybersecurity concepts, hands-on familiarity with security tools, responsible testing practices and a roadmap for continued learning. A good learning journey can look like: fundamentals, networking, Linux, security concepts, vulnerability assessment, web security, ethical hacking, practical labs, reporting and career preparation. This approach helps students build knowledge progressively rather than attempting to learn advanced cybersecurity techniques without the necessary foundation.
Cybersecurity is an evolving field. Organizations increasingly depend on digital systems, cloud platforms, applications, networks and connected technologies. Security professionals therefore need to keep developing their skills as technologies and threats change. For students, starting with a strong foundation can provide time to practise, build projects, explore certifications and develop a professional cybersecurity profile. The goal is simple: learn cybersecurity responsibly, practise in authorized environments, understand the technology behind the tools, and build skills that can support your long-term IT career.
Choosing the right institute can make a major difference when you are starting your cybersecurity journey. Techcadd focuses on helping students build practical, career-oriented IT skills through structured training. For learners searching for ethical hacking training in Amritsar, the program can provide a pathway from fundamental concepts to practical security knowledge.
Ethical hacking is a technical subject, and students can find it difficult if they only study theory. Techcadd's learning approach is designed to make complex cybersecurity concepts easier to understand through structured explanations, demonstrations and practical activities. Students can progressively learn about networking, Linux, security fundamentals, vulnerability assessment, web security and ethical hacking concepts instead of attempting advanced topics without understanding the basics.
You do not need to be an experienced cybersecurity professional to begin learning ethical hacking. Students who have completed 12th, graduates, IT students, freshers and learners interested in cybersecurity can start by developing their technical foundation. The learning journey can progress from computer fundamentals to networking, Linux, cybersecurity basics, security tools, vulnerability assessment, ethical hacking and practical security testing. This progression can help beginners understand not only what a tool does but also why and when it is used.
Cybersecurity employers value practical understanding alongside academic qualifications. That is why practical exposure is an important part of developing cybersecurity skills. During training, learners can work with security-focused technologies and tools in authorized learning environments. Depending on the course curriculum, this may include tools such as Kali Linux, Nmap, Wireshark, Burp Suite and Metasploit. The purpose is to help students understand security assessment processes, interpret findings and develop responsible testing habits.
Techcadd's ethical hacking training is positioned as a career-development program rather than simply a collection of technical lessons. Students can explore different cybersecurity career directions, including security analysis, vulnerability assessment, penetration testing, SOC-related roles and information security. The exact requirements for each job vary, so learners should continue developing their technical skills, communication abilities, practical portfolio and relevant certifications after completing their training.
For students searching for an ethical hacking institute in Amritsar, having access to a local training environment can make learning more convenient. Students can attend training, interact with instructors, ask questions and work through technical problems in a structured environment. This can be particularly useful when learning subjects such as networking, Linux, web security and penetration-testing concepts.
One of the most important principles of cybersecurity training is responsible use. Techcadd can help learners understand that ethical hacking is performed only with appropriate authorization. Security testing should take place in controlled labs, practice environments or systems where explicit permission has been provided. This professional mindset is essential because cybersecurity is not simply about finding vulnerabilities. It is also about protecting systems, documenting findings and helping organizations improve their security posture.
Students should not expect to become cybersecurity experts after completing one course. Ethical hacking is a continuously evolving field that requires regular practice and learning. Techcadd's structured training can serve as a foundation on which students can continue building their cybersecurity knowledge through projects, labs, certifications, internships and further specialization.
If you are looking for an ethical hacking course in Amritsar, ethical hacking classes in Amritsar, or practical cybersecurity training, Techcadd can be considered as a starting point for developing technical skills and exploring a future in information security. The focus should remain on one clear objective: building practical cybersecurity knowledge responsibly and preparing students for continued professional growth in the IT security field.
Collected from students who completed the ethical hacking programme at the Amritsar campus, across morning, evening and weekend batches. Hover a card to stop the row and read it.
5.0
out of 5
10 verified reviews from Amritsar students
I was looking for ethical hacking classes in Amritsar because I wanted to move into cybersecurity. I liked that the training started with networking and Linux before moving into security concepts. The practical exercises made the topics easier to understand.
I had basic computer knowledge but was completely new to ethical hacking. The concepts were explained step by step, which made it easier for me to follow the training. I especially enjoyed learning about Kali Linux and different security tools.
I joined the ethical hacking training to understand cybersecurity better. The course helped me learn networking, Linux, vulnerability assessment and web security concepts. It gave me a much clearer idea about the cybersecurity field.
As an IT student, I wanted something practical alongside my regular studies. Ethical hacking training gave me exposure to tools like Nmap and Wireshark and helped me understand how network security works.
The practical sessions were my favourite part of the training. Instead of only reading about cybersecurity, I could understand how different tools and security concepts work in controlled lab environments. The instructors also explained the concepts in an easy way.
I was exploring different IT career options after graduation and became interested in cybersecurity. The ethical hacking course helped me understand areas such as vulnerability assessment, penetration testing and security analysis. It was useful for understanding what skills I need to develop next.
Initially, Linux and networking seemed difficult to me. The training helped me understand the basics step by step. Once I understood those concepts, learning the cybersecurity tools became much easier.
I wanted to explore cybersecurity before deciding whether to pursue it as a career. The training gave me an introduction to ethical hacking, web security, network security and vulnerability concepts. It helped me understand what the field is actually like.
I had heard about tools like Kali Linux, Burp Suite and Metasploit before joining, but I did not understand their purpose. The training helped me understand how these tools are used in authorized security testing and why cybersecurity fundamentals are important.
My experience with the ethical hacking training was positive. I liked the combination of theory and practical learning. The course helped me build a basic cybersecurity foundation and motivated me to continue learning about penetration testing and information security.
If something here is not covered, the Amritsar desk will answer it directly — no call-back queue.
Ethical hacking is the authorized process of assessing computer systems, networks or applications to identify security weaknesses. Ethical hackers work with permission to help organizations discover vulnerabilities and improve their security.
Book a free demo class and see the lab before you decide.