
Flagship project
Linux & Windows Lab Build
Build and configure a Kali Linux and Windows Server lab environment with documented users, groups and permissions.
- Kali Linux
- VirtualBox
3 / 6 / 9 Months
Duration
Weekday/Weekend
Mode
12th Pass/Any Grad
Eligibility
10-12 Students
Batch Size
Admissions open
Ethical Hacking for Beginners · 3 / 6 / 9 Months
Batch timings
techcadd's Ethical Hacking Course in Ludhiana is a practical, lab-based introduction to offensive security for beginners.
It opens with cybersecurity fundamentals, operating systems and networking, then moves into information gathering, vulnerability assessment, web application security and SOC operations on real targets in a safe lab.
You finish with a portfolio of documented vulnerability reports, CV preparation and interview coaching.
Ethical hacking is the practice of testing systems the way an attacker would, with permission, so the weaknesses are found before someone exploits them. It sits at the centre of every security team's work — penetration tests, vulnerability assessments, red-team exercises, and secure code reviews all depend on people who understand how systems are actually broken into. For someone training in Ludhiana, this is a hands-on, hireable skill rather than a theory course. Manufacturing units, IT firms, banks, and healthcare providers across Punjab are all digitizing their operations, and each of them needs people who can find and report a vulnerability before it becomes a breach.
techcadd's Ethical Hacking for Beginners programme is built around the tools that appear in actual job descriptions — Kali Linux, Burp Suite, Metasploit, Nmap, Wireshark, and OWASP ZAP — not academic substitutes. You work in a hands-on lab from the first week and finish with a portfolio of documented vulnerability reports, not certificates alone. The programme is available in 3, 6, and 9-month tracks, and each longer track includes everything from the shorter one without repeating a module. Batch sizes are capped at 10–12 students, and every deliverable is reviewed weekly by mentors who still work on live engagements.
Core security concepts — the CIA Triad, common threat types, security domains, and the legal and ethical boundaries of ethical hacking.
A written summary of security domains and legal boundaries of ethical hacking
Windows and Linux fundamentals — users, groups, permissions, and the operating system knowledge every security test assumes.
A configured Linux and Windows lab environment with documented permissions
Networking fundamentals — the OSI and TCP/IP models, IP addressing, subnetting, routing, DNS, DHCP, and VPN concepts that every attack and defence depends on.
A documented network map and packet capture analysis
Exploitation workflows with Metasploit and Hydra — password attacks, payloads, and controlled exploitation in the lab.
A documented exploitation walkthrough with remediation notes
Cloud and container security fundamentals — IAM policies, misconfiguration risks, and Docker/Kubernetes hardening.
A cloud security assessment report with misconfiguration findings
Scoping and planning a full security capstone, with documentation from day one.
An approved capstone project plan
Building the core security components of the capstone project in the lab.
A working capstone phase-one build
Hardening Linux systems and networks against the vulnerabilities the earlier modules taught you to find.
A hardened Linux and network configuration report
Build and configure a Kali Linux and Windows Server lab environment with documented users, groups and permissions.
Capture live network traffic with Wireshark and produce a documented network map and packet analysis.
Run OSINT, Google dorking, WHOIS and DNS enumeration against an authorised target and document the findings.
Scan and enumerate with Nmap, Nikto, Nessus and Acunetix, and produce a client-ready vulnerability report with severity ratings.
Test a web application against the OWASP Top 10 with Burp Suite, and document SQL injection, XSS and CSRF findings.
Monitor and triage alerts in a SIEM, map to MITRE ATT&CK, and produce an incident triage report.
Complete an end-to-end capstone combining reconnaissance, scanning, threat detection, controlled exploitation and incident response.
Every project moves through the same loop: understand the brief, build it with guidance, then explain the decisions behind your work. The certificate is the receipt — the portfolio is the point.
You learn it the way it is used on real engagements, with the workflow and standards a security team expects.
Linux & Windows Lab Build
Every module runs in a hands-on lab against real targets — virtual machines, vulnerable apps and packet captures — not screenshots.
Packet Capture & Network Map
Each module ends with a documented artefact reviewed weekly by a mentor who still works on live engagements.
Information Gathering Report
Every exercise ends with a written vulnerability report — the deliverable clients and employers actually pay for.
Vulnerability Assessment Report
A course is worth the time you give it only if you finish with work you can show and skills you can defend.
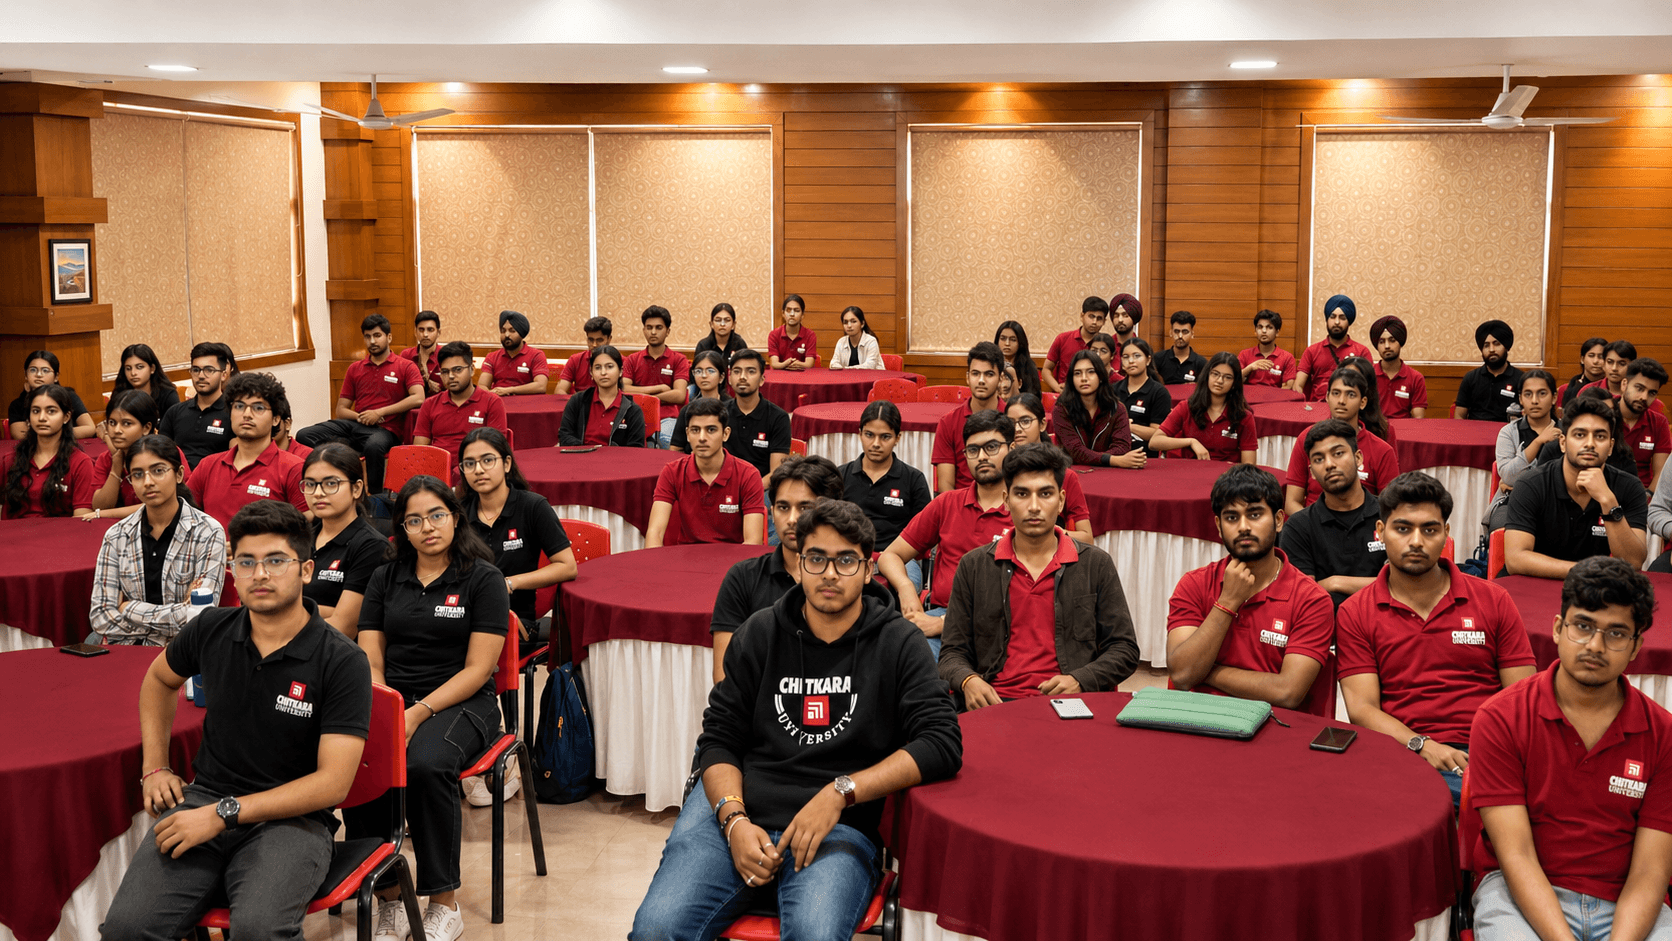
Project review week at the Amritsar campus
Mentors mark up work line by line
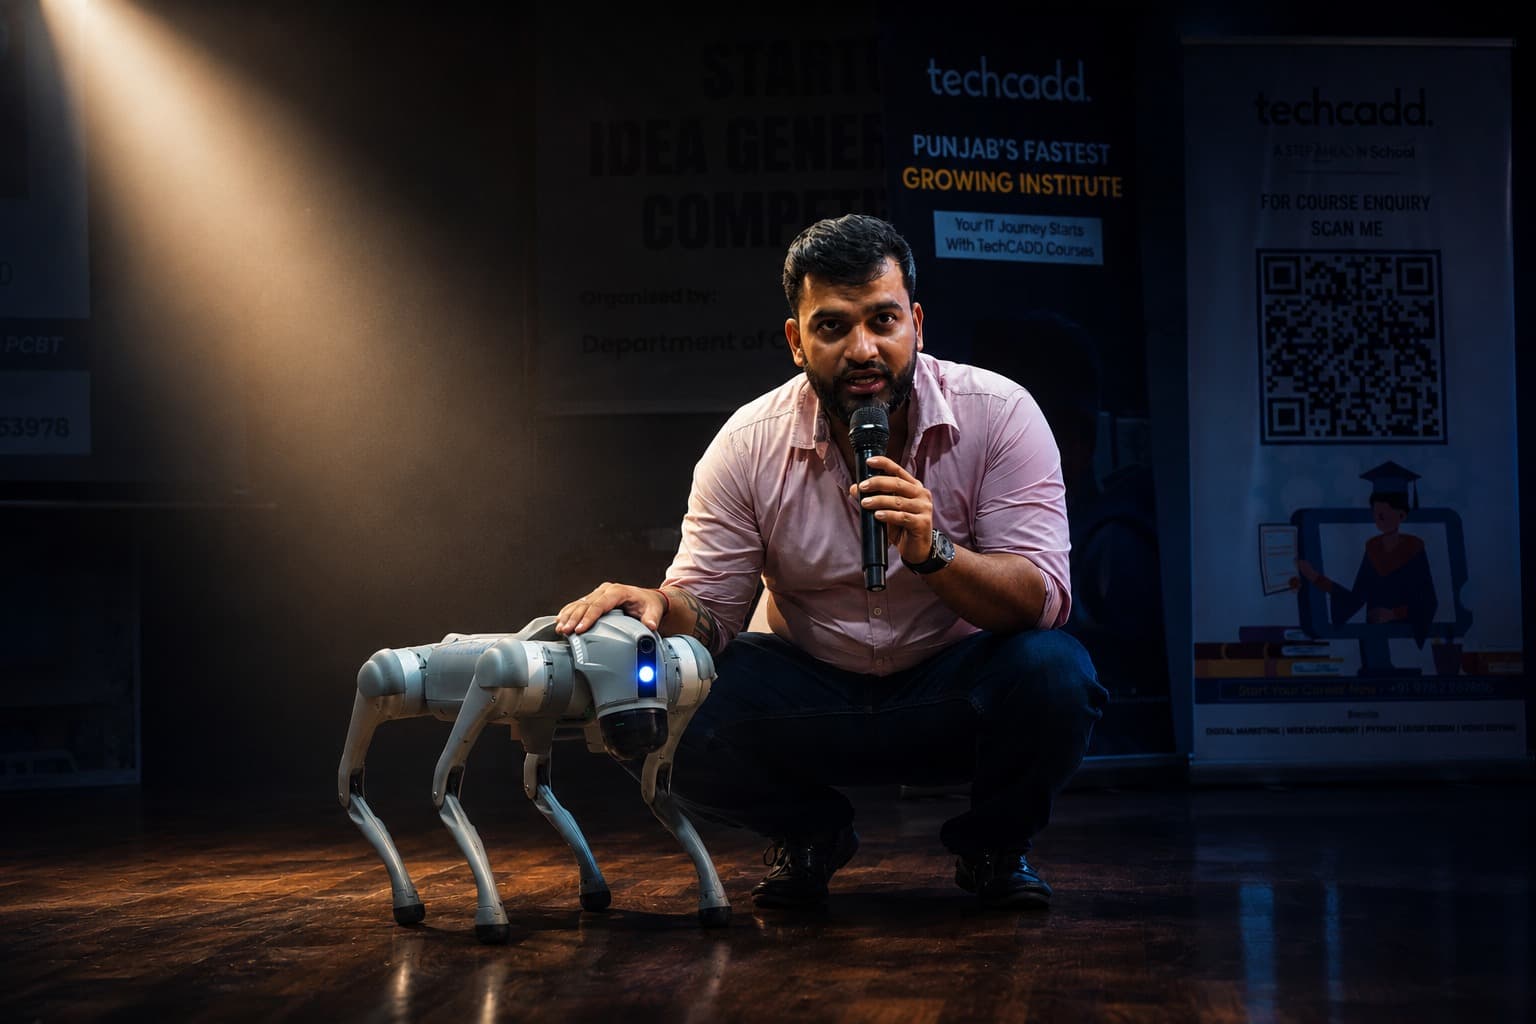
Hiring drive & mock interview day
Practitioners run the panel, not HR
What makes this course at techcadd different from a typical alternative is that every module ends with a written report on a real lab target, so you finish with an end-to-end security portfolio rather than disconnected certificates.
Not full-time lecturers — trainers who are still doing the job they teach.
You build the lab in Module 04, then use it for information gathering, vulnerability assessment, web security and SOC work.
10–12 students per batch ensures every student gets personalised feedback on every deliverable.
Longer programs include everything from shorter tracks and add more depth — you never repeat a module.
Every student receives a documented internship certificate alongside their course certificate.
Resume and LinkedIn preparation, mock interviews, and active placement assistance for graduates
This course works for a specific starting point — here's who gets the most out of it.
Job titles vary by company, but the underlying expectations do not. Each destination below maps to work you will have already done during the programme.
Every tool below is installed, configured and used by you during the course — not demonstrated on a slide. You leave able to set up your own environment from scratch.
20tools covered
Issued on completion against the modules you finished and the projects you submitted — plus an internship letter where the industrial training track applies. Shareable to LinkedIn, and verifiable by an employer who calls the Amritsar desk.
The skill does not stand still, and neither does what it is worth.
The objective is practical knowledge rather than memorised concepts.
What actually differs between this course at techcadd and a typical alternative.
| What you should ask | techcadd Amritsar | Other institutes |
|---|---|---|
| Live lab work | Every module, from week one | Varies, often only at the end |
| Learning format | One lab built in Module 04 and used throughout | Tools demonstrated separately, rarely combined |
| Tools used | Kali Linux, Burp Suite, Metasploit, Nmap, Wireshark, Nessus, Splunk | Usually limited to Nmap and basic scanning |
| Batch size | 10–12 students per batch | Often 25–40 students per batch |
| Web security depth | OWASP Top 10, SQL injection, XSS, CSRF, API testing | Often only theory or a single demo |
| SOC training | Wazuh, Splunk, MITRE ATT&CK with triage reports | Rarely covered |
| Reporting | Every exercise ends with a written client-ready report | Often no reporting practice at all |
| Portfolio | 7 documented lab deliverables | Often just assignments, not portfolio-ready work |
| Certificate | Completion certificate + documented internship | Only a completion certificate |
Every comparison here is about substance, not marketing language.
If something here is not covered, the Amritsar desk will answer it directly — no call-back queue.
No. The programme opens at beginner level and assumes no background beyond comfort with a computer. Students who already have some exposure move through the early modules faster and spend the saved time on project work.
Book a free demo class and see the lab before you decide.